5 Best Penetration Testing Companies in Manchester – Find assessments for digital security weaknesses
A penetration test needs a defined system, permission and business purpose. Manchester providers offer different strengths across applications, networks, cloud environments and specialised connected devices. These five publish Manchester or Greater Manchester premises and relevant testing services. Their numbering is not independent certification or a ranking of technical competence. Verify current credentials and scope before granting access. A test examines agreed targets under agreed conditions; it should not be treated as proof that every security risk has been eliminated.
1. Secarma
Secarma publishes a Manchester registered office and testing across web applications, infrastructure, wireless, mobile and cloud environments. Its service list also separates configuration reviews and scanning from penetration testing. A business can ask which assessment fits the actual question. Request the methodology, manual work, reporting and retesting scope. A broad list of testing capabilities should not be interpreted as inclusion of every system or attack scenario in one engagement.
Published provider information: Secarma
2. Cyphere
Cyphere publishes an Altrincham address in Greater Manchester and penetration testing alongside wider security assessment and managed services. It publishes accreditation claims that should be checked independently for the intended work. A company wanting a defined technical assessment can ask about relevant experience and the actual testers. Distinguish the commissioned test from ongoing monitoring, remediation or certification support. Agree what access the provider needs and how sensitive findings will be protected and communicated.
Published provider information: Cyphere
3. Dalton Cyber
Dalton publishes a Stockport address and Manchester-area penetration-testing services, with advice intended to help clients understand and address weaknesses. A business seeking an assessment can enquire about its particular systems and available evidence. Confirm the tester, technique boundaries and actual remediation support. Identifying an issue, explaining a fix and implementing it are different responsibilities, so the proposal should state which are included rather than leave the client to infer them from a general promise of support.
Published provider information: Dalton Cyber
4. Zenzero — Manchester
Zenzero publishes a Manchester office and security services including penetration testing, vulnerability management and ongoing monitoring. A business already using managed IT can ask whether a separate testing engagement is appropriate. Confirm how assessment findings are reviewed and how potential conflicts are handled if the same provider manages the environment. A combined security service should still make scope, independence, remediation and retesting clear rather than treat all activity as one undifferentiated assurance package.
Published provider information: Zenzero — Manchester
5. You Gotta Hack That
You Gotta Hack That’s company profile publishes Manchester and specialises in Internet of Things, operational technology and embedded systems. Its described services include penetration testing and training for developers and implementers. An organisation with connected devices can ask about relevant technical experience and safe testing conditions. It is a specialist option, not an assumption that every routine website or enterprise environment requires the same expertise. Confirm the actual team, scope and any accreditation independently.
Published provider information: You Gotta Hack That
How to compare the proposed service
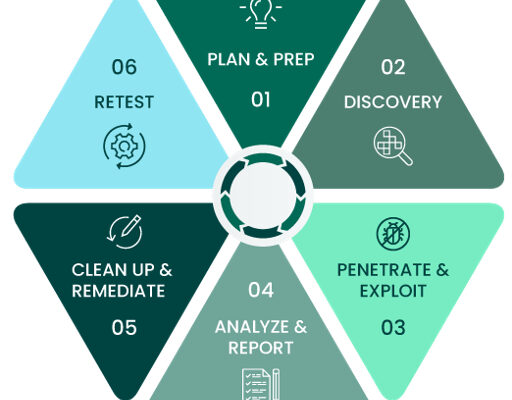
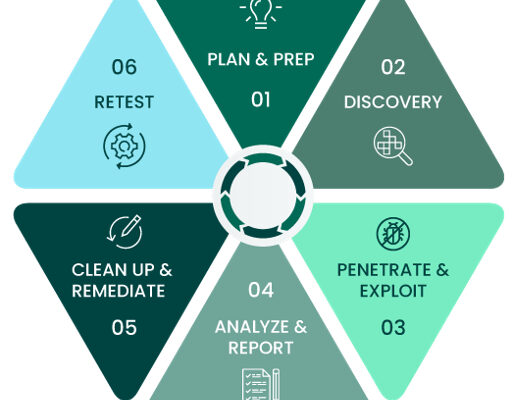
Identify the systems, owners, business impact and question the assessment must answer. Obtain explicit written authorisation for the permitted targets and activity, including relevant third-party arrangements. Agree contacts, timing, stopping conditions and boundaries before testing starts. Do not assume the ability to access a system provides permission to assess it. Distinguish the proposed penetration test from a scanning-only service or a broader simulation.
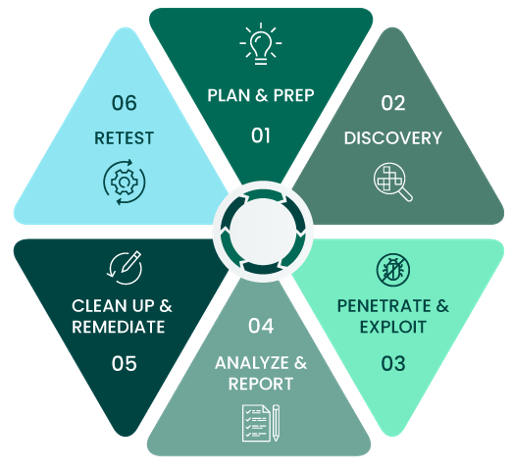
Compare preparation, testing, reporting, explanation, remediation support and retesting separately. Ask how sensitive material is transferred, retained and deleted. Request a report that explains findings, limitations and practical priorities. Verify relevant credentials with the issuing scheme rather than rely on a badge. Treat the work as evidence within its scope and time, not a guarantee of complete protection or an automatic substitute for continuing risk management.
Additional links supplied for this article
All four supplied links are included below. Tech Ventures Sys was retrievable as a general technology publication during this check. Premium IT Vault, Ultra Tech Minds and AI Basic Impacts could not be retrieved, so their contents were not verified. These links are not evidence for provider entries or professional credentials, and inclusion does not imply affiliation, endorsement or an assessment of technical accuracy.
FAQs
Are all five inside Manchester city?
No. Altrincham and Stockport are explicitly identified as Greater Manchester locations.
Does a test include fixing every finding?
Confirm remediation and retesting as separate or explicitly included work.
Can testing begin on verbal assumptions?
Establish written permission, scope and safety arrangements first.
Will a clean report guarantee security?
No. Examine the coverage, conditions and limitations of the assessment.
Make the next enquiry specific
Choose testers around the environment and agreed assessment purpose. Verify credentials, authorisation and reporting before work begins. Assign ownership of improvements and any retest so the engagement produces accountable action rather than a report mistaken for permanent assurance.